
DPDP compliance checklist for CTOs
By Abhijeet Singh · Primary sources verified by dpdprules.orgPublished · Last reviewed 2 min read
What does a CTO need to build for DPDP compliance?
The short answer
The obligations belong to your organisation, not to the CTO, but engineering usually leads the security safeguards, the retention and erasure timers with the 48 hour warning where the Third Schedule applies, the minimum 1 year log retention, breach detection, and the product surfaces for consent withdrawal and rights requests. Most CTO owned work depends on inputs from legal and compliance, so run it as one company plan with explicit dependencies rather than an engineering side quest. None of the rules behind this list is in force as at 29 September 2026: Rules 3, 6, 7, 8 and 14 sit in the group computed to commence 13 May 2027, interpretation until officially confirmed.
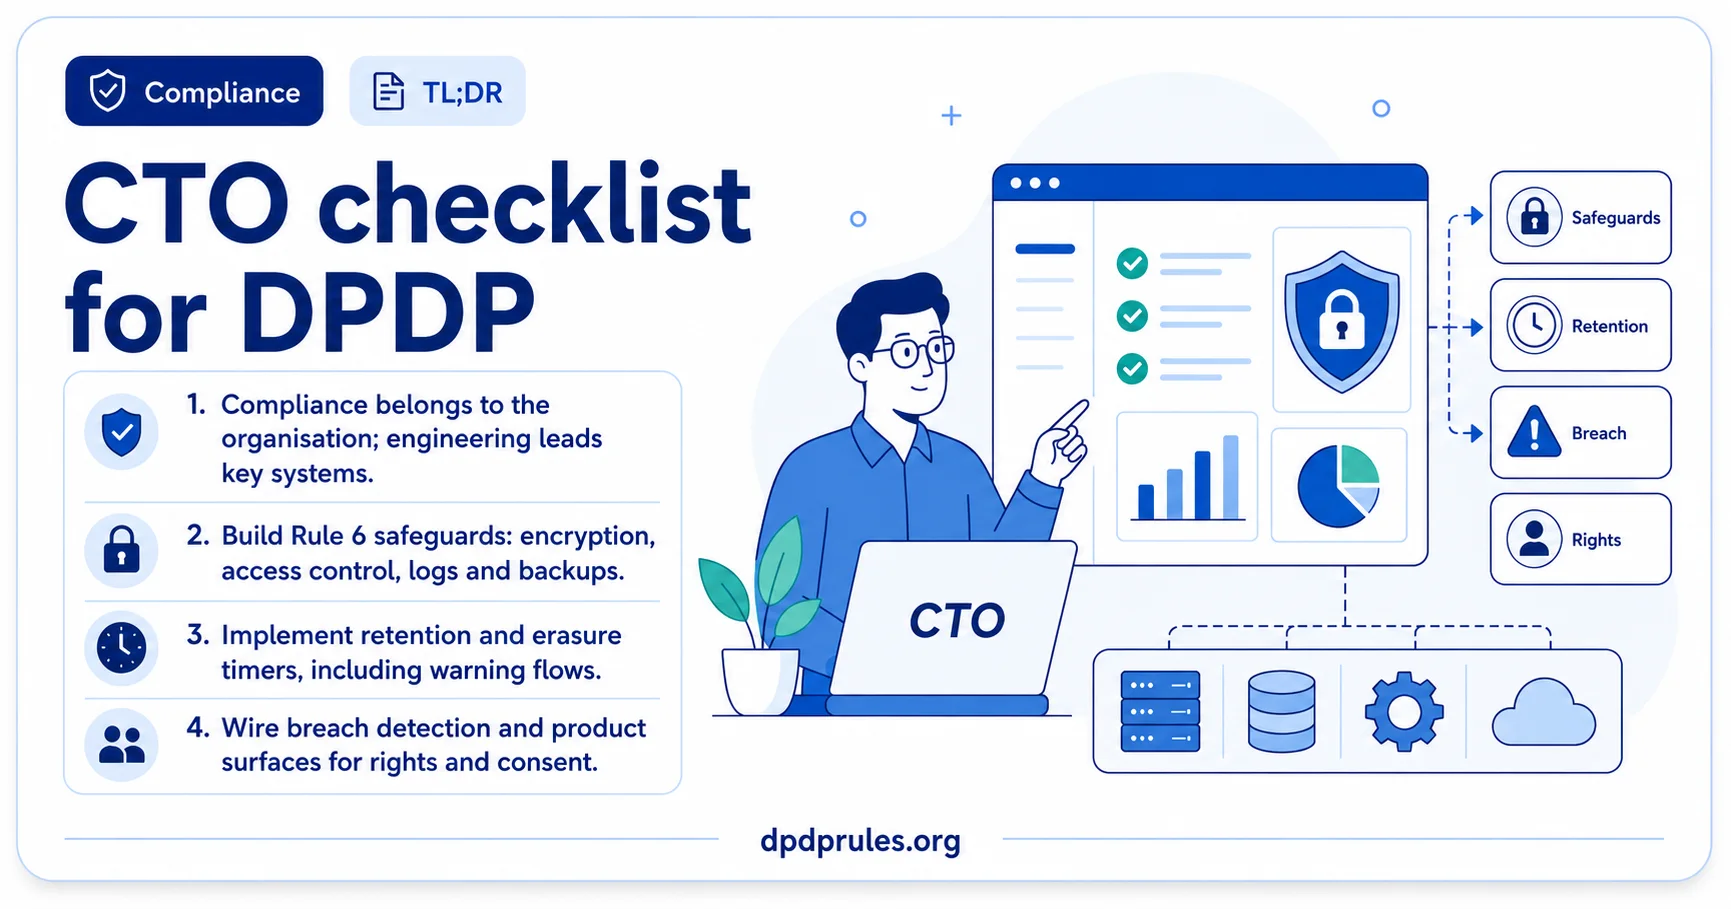
A warning before the checklist: finishing the engineering work does not make the company compliant. The obligations bind the organisation that acts as Data Fiduciary, and legal, compliance and security each own slices. What follows is the slice engineering usually leads, with its dependencies named.
A second warning, about the calendar. Every rule below is in the same commencement group: Rule 1(4) of the DPDP Rules 2025, quoted inline because its closing words are the ones corrigenda G.S.R. 892(E) substituted, says "Rules 3, 5 to 16, 22 and 23 shall come into force eighteen months after the date of publication in the Official Gazette", and Rules 3, 6, 7, 8 and 14 all fall inside that range. So none of the duties on this page is in force today. They commence 18 months after publication, computed at 13 May 2027 and presented as interpretation until officially confirmed. That is a reason to start building rather than a reason to wait, because detection, erasure timers and rights channels are quarters of engineering work, but nothing here is overdue yet and any vendor telling you otherwise is selling urgency.
Build the safeguards floor
Rule 6 names the minimums: encryption, obfuscation, masking or virtual tokens on personal data; access control; log visibility with monitoring and review; backups for continuity; 1 year retention of logs and data; safeguard terms in processor contracts; and organisational measures that keep it all running. Treat it as a control mapping exercise: one named minimum, one control you can point at.
Build the retention machinery
Rule 8 turns retention into system behaviour: erasure timers keyed to purposes for the listed classes, a scheduled warning at least 48 hours before each timed erasure, and a 1 year floor for logs, traffic data and personal data. Dependency: the timers need the retention schedule that compliance and legal design first.
Wire breach detection to the clocks
Both breach duties in Rule 7 start on awareness of a personal data breach, and awareness usually starts in your monitoring. The without delay intimations and the 72 hour detailed Board submission need detection, an escalation path and prepared templates before any incident.
Ship the product surfaces
The notice duties in Rule 3 need engineering delivery: the itemised data description rendered in the flow, withdrawal of consent with ease comparable to giving it, and working paths to exercise rights and complain to the Board. The rights machinery in Rule 14 needs published request channels and identifiers.
Run it as one plan
Every item above has a dependency on another function: the notice needs legal drafting, the timers need the schedule, the Board process needs compliance ownership. Generate the company plan with the CTO lens on: it orders your work first, then shows exactly whose work you are waiting on. The CTO guide has the same map in prose.
Related tool
Compliance Plan
Generate 1 company level action plan and see the work for your role first.
Open
Related tool
Data Breach Response Playbook
Rule 7 is not in force yet, so plan its breach steps now, including the 72 hour submission to the Board, against the exact requirements.
Open
Related tool
Retention and Erasure Planner
Identify DPDP retention and erasure triggers and the action steps for your context.
Open