
Do you need a Data Processor contract under DPDP?
By Abhijeet Singh · Primary sources verified by dpdprules.orgPublished · Last reviewed 5 min read
Jump to sourcesDo I need a contract before engaging a Data Processor under DPDP?
The short answer
Not yet. When section 8(2) commences, a Data Fiduciary may involve a Data Processor only under a valid contract where the processing is on its behalf for an activity related to offering goods or services to Data Principals. Section 17 can change whether that condition applies. Rule 6(1)(f) is the 1 express contract content requirement found in the Act and English Rules: wherever applicable, the contract must contain an appropriate provision for taking reasonable security safeguards. Section 8(1) keeps the fiduciary responsible for processing undertaken on its behalf, and section 8(5) remains applicable under a section 17(1) route. Erasure, retention, breach support, instructions, audit, return and liability can be sensible contract topics, but the Act and Rules do not prescribe them as those Data Processor contract terms. No processor to fiduciary breach deadline is fixed; Rule 7 instead places its clocks on the fiduciary. The operative condition and duties discussed sit in 18 month commencement groups. This site computes 13 May 2027 and treats 15 May 2027 as the outer date because publication records and counting can each move the date by 1 day. Both dates are interpretation until officially confirmed.
Status as at 28 October 2026: section 8(2) and Rule 6(1)(f) are not in force. The computed range is 13 to 15 May 2027, interpretation until officially confirmed.
As at 28 October 2026, the DPDP valid contract condition and safeguards clause rule do not bind yet. When they commence, the answer depends on the processing flow, not merely on whether the supplier calls itself a processor. This page owns that contract decision. For the clause by clause drafting view, see DPA clauses under DPDP.
First decide whether the counterparty is a Data Processor
Section 2(k), which is in force, defines a Data Processor as:
"Data Processor" means any person who processes personal data on behalf of a Data Fiduciary
The role is decided for the processing in question. A supplier can be a processor for 1 flow and a Data Fiduciary for another. If the roles are still open, use the fiduciary and processor role test before testing the contract condition.
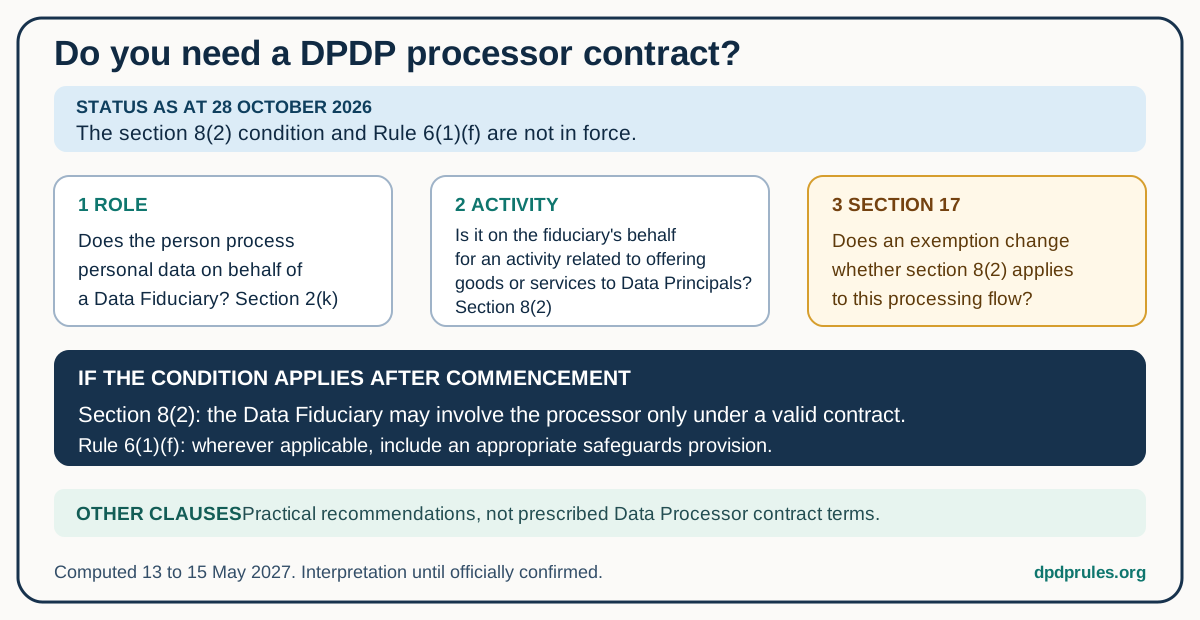
Open the processor contract decision map at full size.
The section 8(2) decision
Section 8(2) states:
"A Data Fiduciary may engage, appoint, use or otherwise involve a Data Processor to process personal data on its behalf for any activity related to offering of goods or services to Data Principals only under a valid contract."
The condition therefore has 3 important limits.
- The processing must be on behalf of a Data Fiduciary.
- The activity must be related to offering goods or services to Data Principals.
- Section 17 must not disapply section 8(2) for that processing.
If those conditions are met after commencement, section 8(2) permits the fiduciary to involve that processor only under a valid contract. It does not say that every person called a processor may act only under a contract, and it does not prescribe a clause list.
The 2 express contract points
The Act and English Rules supply 2 express points for this fiduciary to processor contract.
- Section 8(2): a valid contract is the condition in the processing scope described above.
- Rule 6(1)(f): the minimum reasonable security safeguards include, wherever applicable, an appropriate provision in the contract for taking reasonable security safeguards.
A whole text comparison found Rule 6(1)(f) to be the only express content requirement for that contract. Its words "appropriate" and "wherever applicable" matter. The Rule does not print a universal model clause.
Section 17 can change the answer
Under section 17(1), Chapter II does not apply for its listed processing except sections 8(1) and 8(5). That means section 8(2) can be disapplied while the fiduciary's responsibility under section 8(1) and safeguards duty under section 8(5) survive. Section 17(2) to 17(5) use different routes and scopes, so the section 17 exemptions guide should be applied provision by provision.
Section 17 speaks about provisions of the Act. It does not state how an Act exemption affects related Rules. Any conclusion that section 17 automatically switches a Rule off is therefore interpretation, not printed law.
A contract does not transfer the fiduciary's responsibility
Section 8(1) states:
"A Data Fiduciary shall, irrespective of any agreement to the contrary or failure of a Data Principal to carry out the duties provided under this Act, be responsible for complying with the provisions of this Act and the rules made thereunder in respect of any processing undertaken by it or on its behalf by a Data Processor."
Where section 8(1) applies, a contract can allocate work and commercial risk but cannot displace that responsibility. This is why contract terms are practical controls rather than a substitute for the fiduciary's own compliance.
Other clauses are recommendations, not prescribed terms
Erasure support, retention support, processor breach notice, documented instructions, confidentiality, audit access, return and liability can all be sensible drafting topics. The Act and English Rules do not prescribe them as those Data Processor contract terms.
The underlying duties still need their exact limits. Section 8(7)(b) follows the section 8(7)(a) trigger and the legal retention exception. Rule 8(3) creates a bounded 1 year retention and erasure sequence for Seventh Schedule purposes, not a general 1 year contract clause. Rule 7 places separate without delay duties to affected Data Principals and the Board on the fiduciary, followed by 6 detailed Board items within 72 hours unless the Board allows longer on written request. No processor to fiduciary breach deadline is fixed, so a shorter processor notice window is negotiated protection.
The DPA clauses guide maps those duties and recommendations without presenting them as a statutory clause list.
When the condition starts
Section 8 and section 17 sit in the Act's 18 month group. Rules 6, 7 and 8 sit in the Rules' own 18 month group, with the Rule 1(4) publication wording corrected by G.S.R. 892(E).
Counting from the printed 13 November 2025 date gives 13 May 2027. The official eGazette file code and recorded listing use 14 November 2025, and the instruments do not state how the period is counted, so the date may fall as late as 15 May 2027. Both dates are interpretation until officially confirmed.
What to do now
Map each processing flow, decide the roles, test section 8(2) and section 17, then draft the controls the relationship needs. Work each engagement through the vendor and processor checklist. Read the official wording at section 8, and use Data Processor obligations under DPDP for the processor side of the relationship.
Section 8, official text →Section 17 exemptions, official text →DPA clauses: requirements and recommendations →