
Does the DPDP Act apply to startups? No size test, and 3 places size counts
By Abhijeet Singh · Primary sources verified by dpdprules.orgPublished · Last reviewed 16 min read
Does the DPDP Act apply to startups?
The short answer
On the text, yes, and no size test stands between a startup and the Act. Section 3 applies the Act to the processing of digital personal data within India, and to processing outside India in connection with any activity related to offering goods or services to Data Principals in India, and its only exclusions turn on the kind of processing or on who published the data, never on the size of the organisation. The words turnover, revenue, headcount, small, micro, MSME and threshold appear 0 times in the Act and 0 times in the Rules. Size still decides which duties bite, in 3 places: the Third Schedule attaches the Rule 8(1) erasure timer to 3 classes defined by registered user counts, section 10(1)(a) makes the volume and sensitivity of personal data 1 of the factors behind a Significant Data Fiduciary notification, and section 33(2)(g) makes the likely impact of a penalty on the person a matter the Board weighs. Sitting below the Third Schedule counts is not relief: you keep the section 8(7) purpose test, and this site reads the Rule 8(3) minimum of 1 year as reaching a Data Fiduciary of any size. Section 17(3) names startups, but it is a power to switch off 5 provisions and no notification under it has been located. Section 3 commences 18 months after publication, computed as 13 May 2027, which is interpretation until officially confirmed.
The honest answer is 2 sentences long and neither of them is the one that circulates. On the text, the Act reaches a 2 person company exactly as it reaches a listed one, because its application section never mentions size. Size still decides which duties bite, in 3 places that can be named and cited, and none of them is a startup exemption.
The application test, in the order section 3 asks it
Section 3 is 3 clauses long. 2 of them switch the Act on:
"Subject to the provisions of this Act, it shall— (a) apply to the processing of digital personal data within the territory of India where the personal data is collected–– (i) in digital form; or (ii) in non-digital form and digitised subsequently; (b) also apply to processing of digital personal data outside the territory of India, if such processing is in connection with any activity related to offering of goods or services to Data Principals within the territory of India;"
Read as a test, that is 3 questions and no more:
| Question | Where it comes from | What it does not ask |
|---|---|---|
| Is it personal data, meaning data about an identifiable individual? | section 2(t) | Whether the data is sensitive, financial or health related. The Act has no sensitive category |
| Is it digital, either collected digitally or digitised later? | section 3(a) | Whether you built the system or bought it |
| Is the processing in India, or is it outside India in connection with any activity related to offering goods or services to people in India? | section 3(a) and 3(b) | Where the company is incorporated, or where the founders live |
Nothing in that sequence asks how large the processor is. The identity of the person doing the processing is settled earlier, in the definitions, and it is settled widely. A Data Fiduciary is "any person who alone or in conjunction with other persons determines the purpose and means of processing of personal data", and "person" includes an individual, a firm, an association of persons or a body of individuals "whether incorporated or not", and every artificial juristic person. So on the words of clause (v), 2 founders operating before incorporation are already a person capable of being a Data Fiduciary.
Incorporation is not the gate to being a Data Fiduciary, registration is not the gate, and there is no gate. The 1 role in the framework that does have entry gates is the Consent Manager, and those are gates of incorporation and net worth rather than of applicability, which is a different question from the one this page answers.
That also settles the version of this question founders ask second. A startup with only employees and no customers still processes personal data about identifiable individuals, so it sits inside the same test. The HR and employee data article works through what that means for a payroll and recruitment stack.
What section 3 leaves out, checked word by word
The claim that there is no small business threshold is repeated everywhere and is usually asserted rather than shown. It is worth showing, because the absence is the answer:
| Word searched | Occurrences in the Act | Occurrences in the Rules |
|---|---|---|
| turnover | 0 | 0 |
| revenue | 0 | 0 |
| headcount | 0 | 0 |
| small | 0 | 0 |
| micro | 0 | 0 |
| MSME | 0 | 0 |
| threshold | 0 | 0 |
| startup | 3, all inside section 17(3) and its Explanation | 0 |
Those counts were run over the Gazette print of the Act and the English section of the notified Rules of 13 November 2025, as a case insensitive substring search, so a hit inside a longer word would have been counted too and the 0 for small and micro is a real 0. There is no revenue test, no funding stage test, no employee count test and no user count test in the application section, and no rule creates one.
The 3 places where size counts for a Data Fiduciary
This is the part the standard answer drops. "There is no size threshold" is true of applicability and false of the duty set. Size enters the duties of a Data Fiduciary 3 times, in 3 different ways, and only 1 of them uses a number. There is a 4th size figure in the framework, but it is a gate on a different role: item 4 of Part A of the First Schedule requires an applicant for Consent Manager registration to have a net worth of not less than 2 crore rupees, and item 1 requires it to be a company incorporated in India.
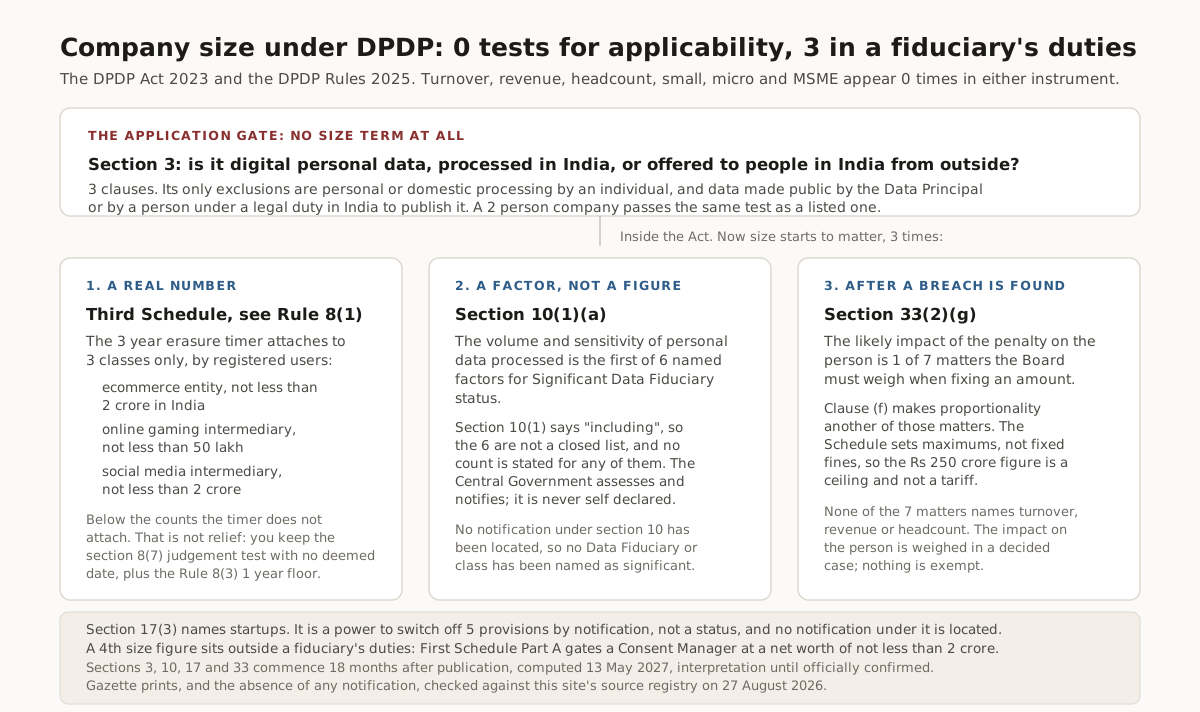
1. The Third Schedule, and it is the only user count. Section 8(8) is the hook. It lets the Rules prescribe how long inactivity must run before a specified purpose is deemed spent, and it says in terms that "different time periods may be prescribed for different classes of Data Fiduciaries and for different purposes". The Third Schedule uses that permission to name 3 classes, and only for the purposes that Schedule lists: an ecommerce entity with not less than 2 crore registered users in India, an online gaming intermediary with not less than 50 lakh, and a social media intermediary with not less than 2 crore. Below those counts the Rule 8(1) erasure timer does not attach to you at all. It is the only place in either instrument where the size of a Data Fiduciary is expressed as a figure, and it is not the relief it looks like: below the counts you lose the deemed date and keep the harder judgement based test in section 8(7), and Rule 8(3) requires, for the purposes specified in the Seventh Schedule, a minimum of 1 year of retention of personal data, associated traffic data and processing logs, with no size qualifier of any kind. That sub rule is addressed to "a Data Fiduciary" and names no class, so this site reads it as binding you whatever your size; the interaction between that open address and the Seventh Schedule purpose limb is not resolved on the face of either text and the point is untested. The retention article sets out both 1 year floors, in Rule 6(1)(e) and Rule 8(3).
2. Significant Data Fiduciary notification, and it is not self assessed. Section 10(1) lets the Central Government notify a Data Fiduciary or class as Significant "on the basis of an assessment of such relevant factors as it may determine, including" 6 named ones, of which clause (a) is "the volume and sensitivity of personal data processed". Volume is therefore a factor, which is the grain of truth behind the belief that large companies get more duties, and the word including means the printed 6 are illustrative rather than a closed list. 2 things about it are routinely lost. The status is created by a government notification and cannot be self declared or self escaped, and no notification under section 10 has been located, so on the record this site holds, no Data Fiduciary or class has been named as significant. If that changes for you, the additional duties are real, and the Significant Data Fiduciary obligations article lists them.
3. Section 33(2)(g), at the penalty stage. The Schedule to the Act sets maximum amounts, and section 33(2) makes the Board have regard to 7 matters when fixing one. Clause (g) is "the likely impact of the imposition of the monetary penalty on the person", and clause (f) makes whether the penalty is proportionate and effective another of those matters. So the answer to whether a 4 person company can really be fined Rs 250 crore is that the figure is a ceiling, the Board is required to weigh the impact on the person before it, and none of the 7 matters mentions turnover. The impact on a small business is something the Board must consider in a decided case; it exempts nothing. The penalties article sets out the Schedule and the Board process article works through section 33(2) in full.
Section 17(3) names startups, and that is a power rather than a status
2 opposite errors circulate here. Some pages say startups are exempt from the DPDP framework. Others correct that by saying no startup exemption exists at all. Both are wrong, and the text is precise:
"The Central Government may, having regard to the volume and nature of personal data processed, notify certain Data Fiduciaries or class of Data Fiduciaries, including startups, as Data Fiduciaries to whom the provisions of section 5, sub-sections (3) and (7) of section 8 and sections 10 and 11 shall not apply."
3 features of that sentence decide the answer. It is a power exercisable by notification, so nothing happens until the Central Government acts and no notification under it has been located. The relief it can give is a closed list of 5 provisions, being notice, accuracy and completeness, erasure and retention, Significant Data Fiduciary duties and the right to access information, so consent, security safeguards, breach intimation, grievance redressal and the children's duties would survive it untouched. And the power is keyed to "the volume and nature of personal data processed", not to company size, which means a startup processing at volume is a poor candidate for it and a large company processing very little is not excluded by the wording.
The Explanation printed under section 17(3) defines a startup, and it defines it by delegation: a private limited company, partnership firm or limited liability partnership incorporated in India which "is eligible to be and is recognised as such in accordance with the criteria and process notified by the department to which matters relating to startups are allocated in the Central Government". Note what that means for anyone checking their own position. The recognition criteria live in a different instrument, issued by that department, and this site has not archived or registered it, so we state the delegation and decline to recite the age and turnover figures that circulate alongside it. Read the recognition notification itself before relying on the route. Section 17 in full covers every other exemption route in the Act, including the separate section 17(5) power and why it is not a grace period.
The exclusions that can actually apply to a startup
Section 3 does have exclusions. They sit in clause (c), and both describe a kind of processing or a publication act rather than a kind of organisation:
"(c) not apply to— (i) personal data processed by an individual for any personal or domestic purpose; and (ii) personal data that is made or caused to be made publicly available by — (A) the Data Principal to whom such personal data relates; or (B) any other person who is under an obligation under any law for the time being in force in India to make such personal data publicly available."
The first limb is narrower than it looks for a founder. It excludes processing by an individual for a personal or domestic purpose, and running a business is neither, so a solo founder's customer list is inside the Act while the same person's contacts app is not. The distinction is the purpose, not the tool, so a personal phone used for customer support does not inherit the exclusion.
The second limb is the one worth reading twice, because a lot of early stage products are built on scraped or aggregated data. Read the words. The data must have been "made or caused to be made publicly available" either by the Data Principal herself, which the section's own Illustration shows with a blogger publishing her views on social media, or by someone under an obligation under a law in force in India to publish it. "Caused to be made" matters, because it reaches a publication she brought about without performing it herself. The same 2 limbs applied to an AI training corpus, where the question becomes a per record one across millions of rows, are worked through in DPDP and AI.
What falls outside both limbs on the words is a publication a third party made on its own initiative, neither caused by the Data Principal nor made under any such legal obligation. Whether data she did publish stays outside the Act once it is compiled and enriched into a product is contested, and this is our reading rather than the section speaking: limb (A) is worded as an attribute of the data, so a compiler can argue the data was made publicly available by her, while the inferred or enriched increment was never made publicly available by her at all. What counts as public data is itself before the Supreme Court in the pending challenge to the Act. The honest answer for a data sourcing plan is that this limb is thinner cover than it is usually treated as, and that the question is open. Section 7 does not rescue it either, since the legitimate uses in section 7 list no publicly available data ground even though the 2022 draft Bill listed 2.
When any of this starts, and the blank that became the runway
Every duty discussed above is in the future, and that is the fact competitors most often get wrong in the present tense. The commencement notification of 13 November 2025 puts the application section itself in the 18 month group:
"eighteen months from the date of publication of this gazette, on which the provision of sections 3 to 5, sub-sections (1) to (8) and (10) of section 6,sections 7 to 10, sections 11 to 17, section 27 except clause (d) of sub-section (1) of the said section, sections 28 to 34, 36, 37 and sub-section (2) of section 44 of the said Act shall come into force."
| For a startup, today | Status |
|---|---|
| Section 2 definitions, so the vocabulary is law | In force since 13 November 2025 |
| Section 3, which applies the Act at all | 18 month group, computed 13 May 2027, interpretation until officially confirmed |
| Chapter II duties in sections 4 to 10, including notice, consent, security and breach intimation, other than section 6(9) | Same 18 month group |
| Section 6(9), registration of a Consent Manager with the Board | 1 year group, computed 13 November 2026, interpretation until officially confirmed |
| Section 17, so the startup exemption power itself | Same 18 month group |
| Sections 28 to 34, so inquiry and penalties | Same 18 month group |
| Rules 3, 5 to 16, 22 and 23, which carry the operational duties | Rule 1(4), 18 months after publication, same computed date |
| Rule 4, Consent Manager registration | Rule 1(3), 1 year after publication, computed 13 November 2026 |
Read the sub section list inside that quote rather than the section ranges, which is a trap this article fell into before review: clause (b) of the same notification lifts section 6(9) out of the 18 month group and puts it, with clause (d) of section 27(1), in the 1 year group. The dates 13 May 2027 and 13 November 2026 are this site's computation from the printed publication date, because both instruments fix a period and neither says how the period is counted. They carry the interpretation label everywhere on this site for that reason, and the 13 versus 14 November question explains why even the start of the count is contested.
Here is the part no competitor page carries, and it changes how the runway should be read. In the draft Rules of 3 January 2025, that runway did not exist. Draft rule 1(2) deferred the operational rules "with effect from" a blank, printed as a run of underscores, with everything else commencing on publication. Once the draft's numbering is mapped onto the notified numbering, the draft's deferred set and the notified 18 month set are the same set, with 1 change: Rule 4 was moved forward into the 1 year group. So a founder reading the draft in January 2025 could not tell whether the operational duties were 1 month away or 3 years away, and the 18 months is a decision taken at notification. Read as a planning fact rather than a legal one, that argues for treating the date as the current answer to an open question rather than as a fixed feature of the framework.
The myths, traced back to the text
| Circulating claim | What the text says |
|---|---|
| Startups are exempt from the DPDP Act | Section 17(3) is a power to notify, its relief is limited to 5 provisions, and no notification under it has been located. Nothing is exempt by being a startup |
| There is no startup exemption in the Act at all | Also wrong. The Act names startups in section 17(3) and defines the term in the Explanation to it. The power exists and is unexercised |
| The Act applies only above a turnover or headcount threshold | The words turnover, revenue, headcount, small, micro, MSME and threshold appear 0 times in the Act and 0 times in the Rules |
| A startup must register with the Data Protection Board | Registration in the framework attaches to Consent Managers only, under section 6(9) and Rule 4. No provision requires a Data Fiduciary to register with the Board or seek approval before processing, though it owes breach intimation under section 8(6) and Rule 7(2), and information the Central Government calls for under section 36 and Rule 23 |
| Every company needs a Data Protection Officer | Section 10(2)(a) binds a Significant Data Fiduciary. Every other Data Fiduciary owes the section 8(9) published contact who can answer questions, prescribed by Rule 9 as prominent publication on the website or app plus a mention in every rights response. The DPO article sets out both tiers |
| Startups must run a Data Protection Impact Assessment | Section 10(2)(c) and Rule 13 place that on a Significant Data Fiduciary. See DPIA under the DPDP Act |
| The 3 year deletion rule applies to everyone | Rule 8(1) attaches to the 3 Third Schedule classes, each defined by a registered user count. Section 8(7) binds everyone and sets no period, and the Rule 8(3) minimum of 1 year has no size qualifier either |
| Startups get a 5 year grace period under section 17(5) | Section 17(5) is a window inside which the Government may act, not a period of exemption. Section 17 in full works it through |
| A small company cannot really be fined Rs 250 crore | The Schedule sets maximums. Section 33(2)(g) makes the likely impact of the penalty on the person a matter the Board must weigh, and clause (f) makes proportionality another. That is a sizing consideration at the penalty stage, not an exemption |
| Compliance is due now | Sections 3 to 17 other than section 6(9), and sections 28 to 34, are in the 18 month group, and section 6(9) is in the 1 year group. Nothing in Chapter II binds any organisation today, and no penalty under section 33 can be imposed today |
What to do with the answer
Settle your own position once, with something you can show a customer or an investor, rather than carrying the question. The applicability check walks section 3 in the order above and records the basis of its answer, and the compliance plan turns the result into the duties that will attach to you and the date each one starts. Because size does change the duty set, the 2 questions worth answering early are whether any Third Schedule class describes what you are building, and whether the volume you are heading towards is the volume section 10(1)(a) is about.
Then work the list rather than the law. The DPDP compliance checklist for startups puts the duties in dependency order for a small team, and the startup guide shows where the framework usually bites a small company first. If you sell to businesses rather than consumers, does DPDP apply to B2B SaaS takes the same section 3 test through a B2B fact pattern, and if the company is incorporated outside India, does DPDP apply to foreign companies works clause (b).
Related tool
Applicability Checker
Find out whether the DPDP framework likely applies to your organisation and processing.
Open
Related tool
Compliance Plan
Generate 1 company level action plan and see the work for your role first.
Open
Section 3, official text with sources →The startup guide →Section 17, every exemption route in the Act →