
Applicability
DPDP Act for ecommerce businesses: checkout, retention and vendors
Apply the DPDP Act to checkout, fulfilment, returns, marketing and vendors, including the special retention rules for large ecommerce platforms.
The 3rd and main DPDP commencement date is computed as 13 May 2027, which is interpretation until officially confirmed. What is in force today
Sources last verified on 28 October 2026. Methodology
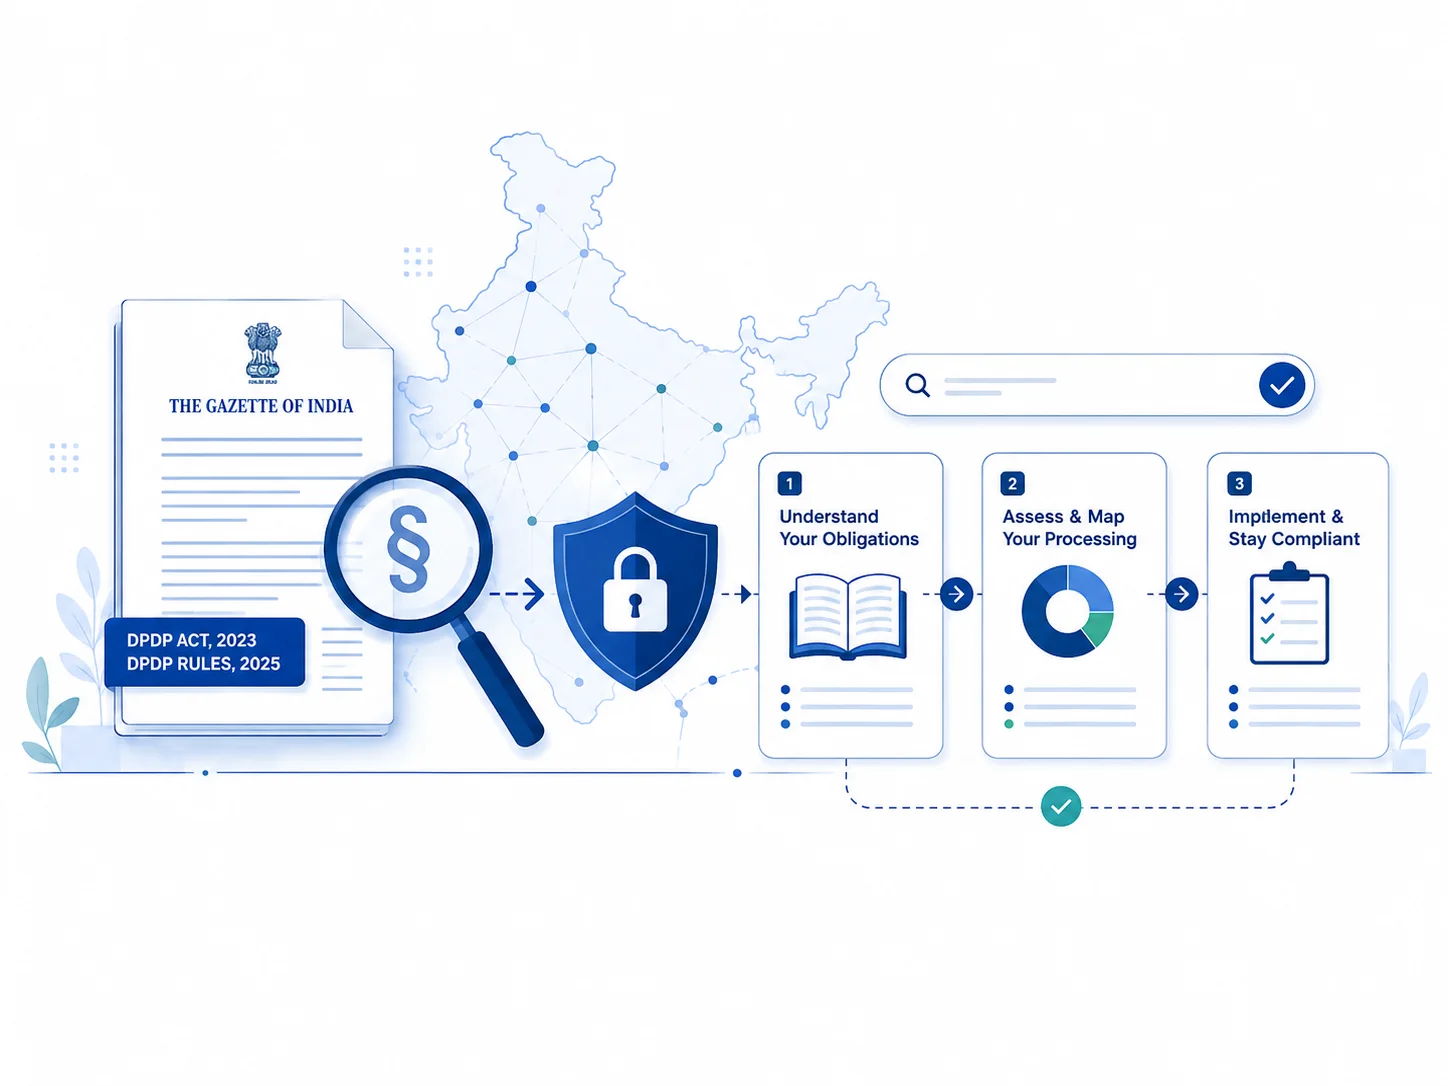
The official Gazette text of all 44 sections, 23 rules and 7 Schedules, their commencement status, 11 deterministic tools, downloadable templates and plain English guides, with every claim cited to the official source. No account, no tracking, no legal jargon.
Plain English
The Digital Personal Data Protection Act 2023 (Act No. 22 of 2023) is India's law on processing digital personal data. Enacted on 11 August 2023, it is coming into force in phases; once section 3 commences, it applies to processing within India and to some processing abroad. The DPDP Rules 2025, published on 13 November 2025, set out how it operates.
Start with the full text of all 44 sections, the glossary of defined terms or the plain English explainer What is the DPDP Act?
Partly. Notification G.S.R. 843(E) brings the Act into force in three groups: 17 of 44 sections are in force today, 25 commence later and 2 are partly in force.
All 23 rules and 7 Schedules →
The official English and Hindi Gazette PDFs are on the documents page.
Applicability Checker
Does DPDP apply?
Role and Actor Checker
What is my role?
Compliance Plan
Company action plan
Data Breach Response Playbook
Breach playbook
Privacy Notice Checker
Notice coverage
Privacy Notice Generator
Notice draft
Retention and Erasure Planner
Retention triggers
Children's Data Checker
Child data duties
Vendor and Processor Checklist
Vendor actions
DPDP vs GDPR Gap Checker
Gap review
Individual Rights Assistant
Your rights
Work out whether the Act applies, build a company action plan, and be ready for the 72 hour breach clock.
Understand the rights the Act gives you over your personal data and the channels every Data Fiduciary must offer.
DPDP stands for Digital Personal Data Protection. The Digital Personal Data Protection Act 2023, Act No. 22 of 2023, is India's law for processing digital personal data; it received the President's assent on 11 August 2023 and recognises both the individual's right to protect personal data and the need to process it for lawful purposes. The DPDP Rules 2025, notified on 13 November 2025, operationalise the Act. Both commence in phases: some provisions have been in force since 13 November 2025, Consent Manager registration is due on a computed date of 13 November 2026, and the main obligations are due on a computed date of 13 May 2027, both interpretation until officially confirmed. Once section 3 is in force with the main obligations, the law applies to digital personal data processed in India, and to processing abroad in connection with any activity related to offering goods or services to people in India, but not to personal or domestic processing or to data made publicly available by the individual or under a legal duty (section 3(c)).
The DPDP Act 2023 was enacted on 11 August 2023 and its commencement was notified as G.S.R. 843(E) on 13 November 2025: the definitions, the sections establishing and constituting the Data Protection Board (sections 18 to 26) and certain other sections, including the rule making power, operate now, while the main obligations, the rights and the Board's inquiry and penalty powers follow 18 months after publication. The DPDP Rules 2025 were notified the same day, and Rules 1, 2 and 17 to 21 took effect at once. The main operational obligations in Rules 3, 5 to 16, 22 and 23 and the core Act sections follow 18 months after publication, which computes to 13 May 2027, and Rule 4 on Consent Manager registration and obligations, and sections 6(9) and 27(1)(d) of the Act, follow 1 year after publication, which computes to 13 November 2026. The computed dates are interpretation until officially confirmed. The Board has been established, but as at 21 October 2026 no appointment of its Chairperson or Members has been located, in a search of official channels on 28 August 2026 or in MeitY's published document library as enumerated on 21 October 2026, and on 7 October 2026 the Union's counsel told the High Court of Kerala that the Board has yet to be made functional.
Once section 33 is in force, the Data Protection Board may impose a monetary penalty specified in the Act's Schedule if, on concluding an inquiry, it determines a breach of the Act or Rules is significant, after giving the person an opportunity of being heard. Each figure is a maximum: 250 crore rupees for the section 8(5) obligation to take reasonable security safeguards; 200 crore rupees each for the section 8(6) breach intimation obligation and for the additional obligations relating to children under section 9; 150 crore rupees for a Significant Data Fiduciary's additional obligations under section 10; 10,000 rupees for the duties under section 15; 50 crore rupees for any other provision of the Act or Rules; and, for breach of a voluntary undertaking accepted under section 32, up to the cap for the breach whose section 28 proceedings were instituted. Sections 8 to 10, 15 and 28 to 34 are in the 18 month group of G.S.R. 843(E), computed at 13 May 2027, interpretation until officially confirmed; the Schedule commencing with section 33 is this site's reading. At 24 October 2026 no penalty can be imposed because section 33 has not commenced. Separately, no appointment of a Chairperson or Member was located in MeitY's published document library through 24 October 2026. The wider 28 August 2026 search of official channels was not repeated and the eGazette search was not queried, so the appointment finding is not a certified negative.
Yes, once it commences. Section 3(a) covers processing of digital personal data within India and section 3(b) processing outside India in connection with any activity related to offering of goods or services to Data Principals within India; on this site's reading, offshore the test is what is offered to people in India, not merely having Indian users. Section 3 commences 18 months after publication of G.S.R. 843(E), computed as 13 May 2027, interpretation until officially confirmed. On this site's reading the Act sets no general local presence duty: representative, subsidiary and branch each appear 0 times in it. The India specific exceptions are narrow: once section 10 commences, a notified Significant Data Fiduciary must appoint a Data Protection Officer based in India, and once Rule 4 commences on the computed date of 13 November 2026, interpretation until officially confirmed, an applicant to register as a Consent Manager must be a company incorporated in India. Section 8(9) will require published contact details of a person able to answer questions, not that the person be in India. On this site's reading, the lever against a company with no Indian assets is section 37, in the same group: once in force, on a Board reference intimating monetary penalty in 2 or more instances and advising blocking in the public interest, and after a hearing, the Central Government may order blocking of public access to information in any computer resource enabling it to offer goods or services in India.
On the text, yes, and no size test stands between a startup and the Act. Section 3 and every provision cited below commence on the computed date of 13 May 2027, interpretation until officially confirmed, so none is in force yet. Section 3 will reach processing within India and offshore processing in connection with any activity related to offering goods or services to Data Principals in India. Its exclusions, for personal or domestic purposes of an individual and for data made public by the Data Principal or under a legal duty, never turn on size. Turnover, revenue, headcount, small, micro, MSME and threshold appear 0 times in the Act and the English Rules. Size can still matter: the Third Schedule attaches the Rule 8(1) erasure timer to 3 classes of e commerce, online gaming and social media platforms defined by registered user thresholds in India, section 10(1)(a) makes volume and sensitivity of personal data 1 of an open list of Significant Data Fiduciary factors, and section 33(2)(g) makes a penalty's likely impact on the person a matter the Board weighs. Falling outside the Third Schedule is not relief: the section 8(7) erasure duty remains, and this site reads the Rule 8(3) minimum of 1 year as reaching a Data Fiduciary of any size. Section 17(3) names startups, but only as a power to notify relief from 5 provisions, and no such notification had been located as at 9 October 2026.
Once section 6 is in force, consent must be free, specific, informed, unconditional and unambiguous with a clear affirmative action, signify agreement to processing for the specified purpose, and be limited to the personal data necessary for it. Any part of a consent that infringes the Act, its rules or any other law in force is invalid to that extent. Each consent request must be in clear and plain language, give the Data Principal the option to access it in English or any Eighth Schedule language, and provide contact details of a Data Protection Officer, where applicable, or of another person authorised to respond about her rights. Where consent is the basis of processing, she may withdraw it at any time, with ease comparable to giving it. On withdrawal, the Data Fiduciary must, within a reasonable time, cease, and cause its Data Processors to cease, processing personal data of hers unless processing without consent is required or authorised under the Act, the rules or any other law in force in India. Where consent is the basis and a question arises in a proceeding, that is, Board action, the Data Fiduciary must prove notice was given and consent was given as the Act and rules require. As at 2 October 2026 no part of section 6 is in force; sub sections (1) to (8) and (10) commence 18 months after publication, computed 13 May 2027, and (9) after 1 year, computed 13 November 2026, both interpretation until officially confirmed.
Both, because they are 2 separate legal regimes with different recipients. Under Rule 7 of the DPDP Rules 2025, once it is in force, a Data Fiduciary must intimate each affected Data Principal and send the Data Protection Board a description of the breach without delay, then file detailed information with the Board within 72 hours of becoming aware, or any longer period the Board allows on a written request. Separately, under the CERT In directions of 28 April 2022 issued under the IT Act, service providers, intermediaries, data centres, body corporates and government organisations must report cyber incidents listed in Annexure I, which includes data breach and data leak, to CERT In within 6 hours of noticing them. The DPDP duty is in the commencement group computed to 13 May 2027, interpretation until officially confirmed; the CERT In duty is already in effect: the directions took effect 60 days after issue, and on 25 September 2022 for MSMEs.
Applicability
Apply the DPDP Act to checkout, fulfilment, returns, marketing and vendors, including the special retention rules for large ecommerce platforms.
Applicability
Map each fintech data flow by purpose and means, then apply consent, contracts, the loan default exemption, retention, the RBI draft and live IRDAI rules.
Children
Supreme Court, 20 July 2026: APAAR processing is governed by the DPDP Act. The order cites 0 sections; section 9 commences on a computed 13 May 2027, interpretation until confirmed.
Every claim is cited
Each legal statement links to the official source it comes from: the Gazette of India, India Code or MeitY, and EUR Lex for GDPR comparisons, with the page number where the source is a fixed document and the date we last verified it.
Results are decided by rules, not vibes
Tool answers come from a published rulebook. Every result shows the rule IDs and facts that produced it. Same inputs, same answer, every time.
Your data stays with you
Assessments run in your browser and are stored only on your device. No account, no analytics on your answers, one click to erase.
Edited and accountable
Edited by Abhijeet Singh. Sources last verified on 28 October 2026. All 8 corrigendum corrections to the Rules, and the 2 word substitutions S.O. 5458(E) made in the Act, are shown against the original text, and anything wrong here is a report away from being fixed. Status last checked 29 October 2026 against the MeitY library and India Code.